
Gaming · 6 views
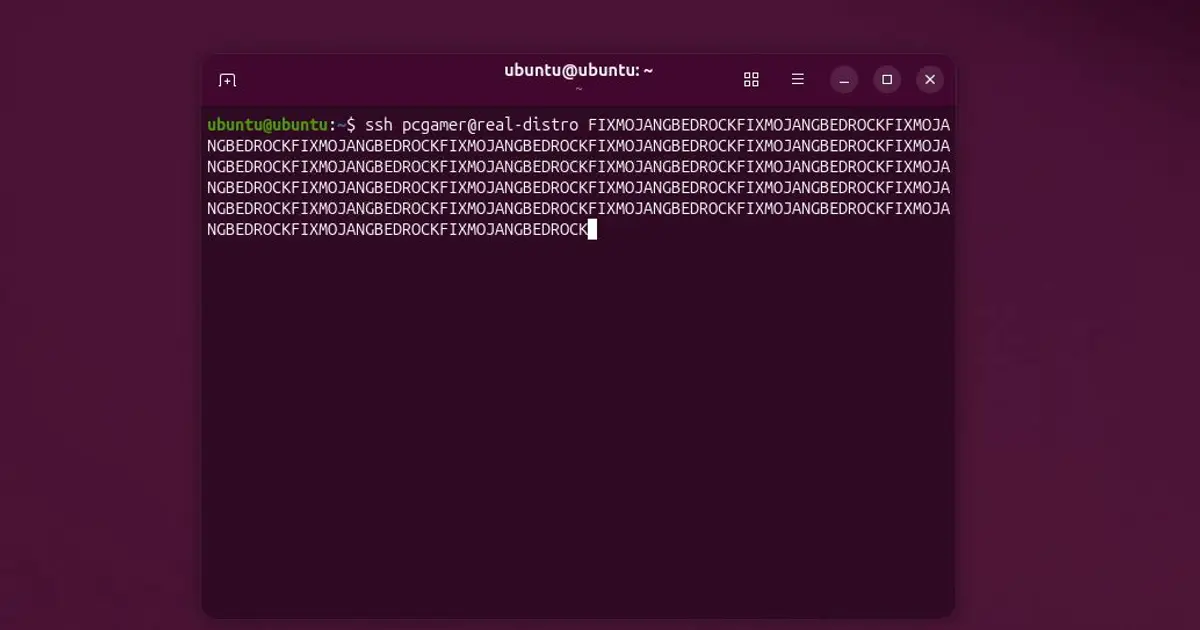
All that stands between a hacker and admin privileges on some Linux distros is a 257-character long string of literally anything
Some implementations of secure shell (SSH), one of Linux's most trusted and secure connection protocols, have been found vulnerable to the most peculiarly simple methods of bypass: spamming characters.

AI Summary
Researchers discovered that certain Linux distributions’ SSH implementations can be bypassed by entering a long string of characters—any 257 to 1,024 characters—allowing immediate root login. The vulnerability affects a small, niche set of distros rather than mainstream systems. OpenSSH has responded by releasing a workaround and a fix to close the flaw. The issue highlights how even trusted protocols can be compromised by unusually simple input methods.
AI summaries can be wrong sometimes—always verify important details using the source article.
How AI & Automation are usedMore from Gaming
Continue reading recent Gaming coverage
- Cat-Astrophy: How a Build Can Change Every ExpeditionContinue reading
- There’s A New DMZ Map Hidden In MW4, And Here’s How To Find ItContinue reading
- Mass Effect Is Getting A New Art Collection At A Difficult Time For Its FansContinue reading
- It's hard to meet women when I keep teleporting all the timeContinue reading
Support HappeningNow
Independent AI-powered news analysis is reader-supported. Your contribution helps cover infrastructure, summaries, and continued platform development.
Support HappeningNow